IT Governance An International Guide to Data Security and ISO 27001/ISO 27002
-
- Hardcover ausgewählt
- Taschenbuch
- eBook
-
Sprache:Englisch
-
Verlag:Kogan Page Ltd
- ITGP 102,99 €
- Kogan Page Ltd 264,99 € ausgewählt
264,99 €
inkl. gesetzl. MwSt.,
Beschreibung
Produktdetails
Einband
Gebundene Ausgabe
Erscheinungsdatum
03.10.2019
Verlag
Kogan Page LtdSeitenzahl
408
Maße (L/B/H)
24/16,1/3,1 cm
Gewicht
935 g
Auflage
7
Sprache
Englisch
ISBN
978-1-78966-030-2
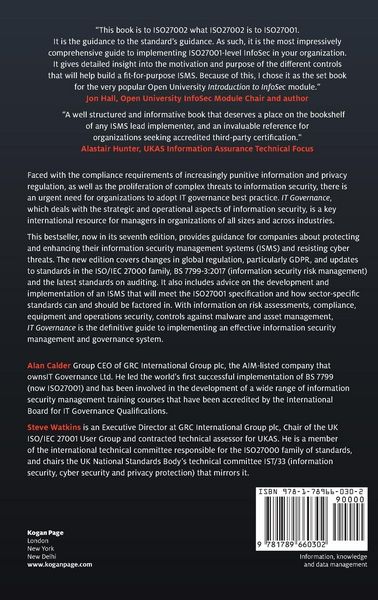
Faced with the compliance requirements of increasingly punitive information and privacy-related regulation, as well as the proliferation of complex threats to information security, there is an urgent need for organizations to adopt IT governance best practice.
IT Governance
is a key international resource for managers in organizations of all sizes and across industries, and deals with the strategic and operational aspects of information security.
Now in its seventh edition, the bestselling
IT Governance
provides guidance for companies looking to protect and enhance their information security management systems (ISMS) and protect themselves against cyber threats. The new edition covers changes in global regulation, particularly GDPR, and updates to standards in the ISO/IEC 27000 family, BS 7799-3:2017 (information security risk management) plus the latest standards on auditing. It also includes advice on the development and implementation of an ISMS that will meet the ISO 27001 specification and how sector-specific standards can and should be factored in. With information on risk assessments, compliance, equipment and operations security, controls against malware and asset management,
IT Governance
is the definitive guide to implementing an effective information security management and governance system.
Noch keine Bewertungen vorhanden
Verfassen Sie die erste Bewertung zu diesem Artikel
Helfen Sie anderen Kundinnen und Kunden durch Ihre Meinung.
Kurze Frage zu unserer Seite
Vielen Dank für Ihr Feedback
Wir nutzen Ihr Feedback, um unsere Produktseiten zu verbessern. Bitte haben Sie Verständnis, dass wir Ihnen keine Rückmeldung geben können. Falls Sie Kontakt mit uns aufnehmen möchten, können Sie sich aber gerne an unseren Kund*innenservice wenden.
zum Kundenservice