KI-Beratung Beta

Gutscheinbedingungen

**Gültig bis 11.11.2026 auf Spielzeug, Schreibwaren, Filme, Geschenke & Trends, Musik, tolino eReader & Zubehör, Hörbücher und Hörbuch-Downloads, nicht preisgebundene Bücher und Kalender online auf thalia.at und in der Thalia App. Einzelne Artikel können ausgeschlossen sein. Aufgrund der Buchpreisbindung sind deutschsprachige Bücher und eBooks ausgenommen. Zusätzlich ausgenommen sind Abos & Flatrates, Games, Geschenkkarten/-boxen, Shelfies, Software, Zeitschriften sowie einzelne Artikel von tonies®. Pro Einkauf einmal einlösbar. Click & Collect nur bei Onlinevorabzahlung möglich. Keine Barauszahlung. Nicht kombinierbar mit anderen Aktionen und Gutscheinen. Gutschein wird auf max. 500€ Bestellwert angerechnet. Nicht gültig für Versandkosten und Services.

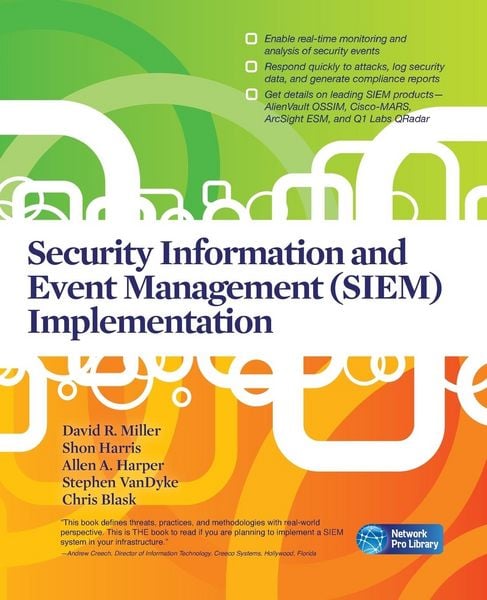
Produktbild: Security Information and Event Management (SIEM) Implementation

Security Information and Event Management (SIEM) Implementation

108,99 €

inkl. gesetzl. MwSt., Versandkostenfrei


Beschreibung

Publisher's Note: Products purchased from Third Party sellers are not guaranteed by the publisher for quality, authenticity, or access to any online entitlements included with the product.

Implement a robust SIEM system

Effectively manage the security information and events produced by your network with...

Beschreibung

Publisher's Note: Products purchased from Third Party sellers are not guaranteed by the publisher for quality, authenticity, or access to any online entitlements included with the product.


Implement a robust SIEM system

Effectively manage the security information and events produced by your network with help from this authoritative guide. Written by IT security experts, Security Information and Event Management (SIEM) Implementation shows you how to deploy SIEM technologies to monitor, identify, document, and respond to security threats and reduce false-positive alerts. The book explains how to implement SIEM products from different vendors, and discusses the strengths, weaknesses, and advanced tuning of these systems. You'll also learn how to use SIEM capabilities for business intelligence. Real-world case studies are included in this comprehensive resource.


  • Assess your organization's business models, threat models, and regulatory compliance requirements

  • Determine the necessary SIEM components for small- and medium-size businesses

  • Understand SIEM anatomy-source device, log collection, parsing/normalization of logs, rule engine, log storage, and event monitoring

  • Develop an effective incident response program

  • Use the inherent capabilities of your SIEM system for business intelligence

  • Develop filters and correlated event rules to reduce false-positive alerts

  • Implement AlienVault's Open Source Security Information Management (OSSIM)

  • Deploy the Cisco Monitoring Analysis and Response System (MARS)

  • Configure and use the Q1 Labs QRadar SIEM system

  • Implement ArcSight Enterprise Security Management (ESM) v4.5

  • Develop your SIEM security analyst skills

Produktdetails

Einband

Taschenbuch

Erscheinungsdatum

15.11.2010

Abbildungen

Illustrationen, nicht spezifiziert

Verlag MCGRAW-HILL Professional

Produktdetails

Einband

Taschenbuch

Erscheinungsdatum

15.11.2010

Abbildungen

Illustrationen, nicht spezifiziert

Verlag MCGRAW-HILL Professional
Seitenzahl

466

Maße (L/B/H)

23,5/19,1/2,5 cm

Gewicht

863 g

Sprache

Englisch

ISBN

978-0-07-170109-9

Herstelleradresse

Libri GmbH
Europaallee 1
36244 Bad Hersfeld
DE

Email: gpsr@libri.de

Noch keine Bewertungen vorhanden

Verfassen Sie die erste Bewertung zu diesem Artikel

Helfen Sie anderen Kundinnen und Kunden durch Ihre Meinung.

Kundinnen und Kunden meinen

Bewertungen (0)

  • Produktbild: Security Information and Event Management (SIEM) Implementation
  • Part I: Introduction to SIEM: Threat Intelligence for IT Systems
    Chapter 1 Business Models
    Chapter 2 Threat Models
    Chapter 3 Regulatory Compliance
    Part II: IT Threat Intelligence Using SIEM Systems
    Chapter 4 SIEM Concepts - Components for small and medium size businesses
    Chapter 5 The Anatomy of a SIEM
    Chapter 6 Incident Response
    Chapter 7 Using SIEM for Business Intelligence
    Part III: SIEM Tools
    Chapter 8 AlienVault OSSIM Implementation
    Chapter 9 AlienVault OSSIM Operation
    Chapter 10 Cisco Security-MARS Implementation
    Chapter 11 Cisco Security-MARS Advanced Techniques
    Chapter 12 Q1 Labs QRadar Implementation
    Chapter 13 Q1 Labs QRadar Advanced Techniques
    Chapter 14 ArcSight Implementation
    Chapter 15 ArcSight ESM Advanced Techniques
    Appendix: The Ways and Means of the Security Analyst