KI-Beratung Beta

Gutscheinbedingungen

**Gültig am 20.11.2026 ab einem Mindestbestellwert von 30€ auf Spielzeug, Schreibwaren, Filme, Geschenke & Trends, Musik, tolino eReader & Zubehör, Hörbücher und Hörbuch-Downloads, nicht preisgebundene Bücher und Kalender online auf thalia.at und in der Thalia App. Einzelne Artikel können ausgeschlossen sein. Aufgrund der Buchpreisbindung sind deutschsprachige Bücher und eBooks ausgenommen. Zusätzlich ausgenommen sind Abos & Flatrates, Games, Geschenkkarten/-boxen, Shelfies, Software, Zeitschriften sowie einzelne Artikel von tonies®. Pro Einkauf einmal einlösbar. Click & Collect nur bei Onlinevorabzahlung möglich. Keine Barauszahlung. Nicht kombinierbar mit anderen Aktionen und Gutscheinen. Gutschein wird auf max. 500€ Bestellwert angerechnet. Nicht gültig für Versandkosten und Services. Preisgebundene Artikel sind vom Mindestbestellwert ausgeschlossen.

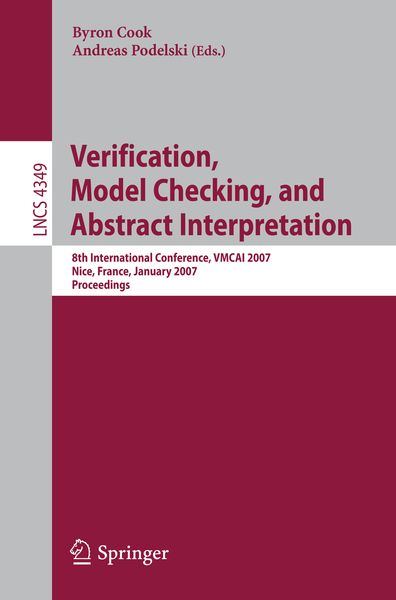
  • Produktbild: Verification, Model Checking, and Abstract Interpretation
  • Produktbild: Verification, Model Checking, and Abstract Interpretation
Band 4349

Verification, Model Checking, and Abstract Interpretation 8th International Conference, VMCAI 2007, Nice, France, January 14-16, 2007, Proceedings

51,99 €

inkl. gesetzl. MwSt., Versandkostenfrei


Beschreibung

Invited Talk.- DIVINE: DIscovering Variables IN Executables.- Session 1.- Verifying Compensating Transactions.- Model Checking Nonblocking MPI Programs.- Model Checking Via ?CFA.- Using First-Order Theorem Provers in the Jahob Data Structure Verification System.- Invited Tutorial.- Interpolants and...

Beschreibung

Invited Talk.- DIVINE: DIscovering Variables IN Executables.- Session 1.- Verifying Compensating Transactions.- Model Checking Nonblocking MPI Programs.- Model Checking Via ?CFA.- Using First-Order Theorem Provers in the Jahob Data Structure Verification System.- Invited Tutorial.- Interpolants and Symbolic Model Checking.- Session 2.- Shape Analysis of Single-Parent Heaps.- An Inference-Rule-Based Decision Procedure for Verification of Heap-Manipulating Programs with Mutable Data and Cyclic Data Structures.- On Flat Programs with Lists.- Invited Talk.- Automata-Theoretic Model Checking Revisited.- Session 3.- Language-Based Abstraction Refinement for Hybrid System Verification.- More Precise Partition Abstractions.- The Spotlight Principle.- Lattice Automata.- Invited Tutorial.- Learning Algorithms and Formal Verification (Invited Tutorial).- Session 4.- Constructing Specialized Shape Analyses for Uniform Change.- Maintaining Doubly-Linked List Invariants in Shape Analysis with Local Reasoning.- Automated Verification of Shape and Size Properties Via Separation Logic.- Invited Talk.- Towards Shape Analysis for Device Drivers.- Session 5.- An Abstract Domain Extending Difference-Bound Matrices with Disequality Constraints.- Cibai: An Abstract Interpretation-Based Static Analyzer for Modular Analysis and Verification of Java Classes.- Symmetry and Completeness in the Analysis of Parameterized Systems.- Better Under-Approximation of Programs by Hiding Variables.- Invited Tutorial.- The Constraint Database Approach to Software Verification.- Session 6.- Constraint Solving for Interpolation.- Assertion Checking Unified.- Invariant Synthesis for Combined Theories.

Produktdetails

Einband

Taschenbuch

Erscheinungsdatum

03.01.2007

Abbildungen

XI, 395 p.

Herausgeber Byron Cook + weitere

Produktdetails

Einband

Taschenbuch

Erscheinungsdatum

03.01.2007

Abbildungen

XI, 395 p.

Herausgeber
Verlag Springer Berlin
Seitenzahl

395

Maße (L/B/H)

23,5/15,5/2,3 cm

Gewicht

622 g

Auflage

2007

Sprache

Englisch

ISBN

978-3-540-69735-0

Herstelleradresse

Springer-Verlag KG
Sachsenplatz 4-6
1201 Wien
AT

Email: ProductSafety@springernature.com

Noch keine Bewertungen vorhanden

Verfassen Sie die erste Bewertung zu diesem Artikel

Helfen Sie anderen Kundinnen und Kunden durch Ihre Meinung.

Kundinnen und Kunden meinen

Bewertungen (0)

  • Produktbild: Verification, Model Checking, and Abstract Interpretation
  • Produktbild: Verification, Model Checking, and Abstract Interpretation
  • Invited Talk.- DIVINE: DIscovering Variables IN Executables.- Session 1.- Verifying Compensating Transactions.- Model Checking Nonblocking MPI Programs.- Model Checking Via ?CFA.- Using First-Order Theorem Provers in the Jahob Data Structure Verification System.- Invited Tutorial.- Interpolants and Symbolic Model Checking.- Session 2.- Shape Analysis of Single-Parent Heaps.- An Inference-Rule-Based Decision Procedure for Verification of Heap-Manipulating Programs with Mutable Data and Cyclic Data Structures.- On Flat Programs with Lists.- Invited Talk.- Automata-Theoretic Model Checking Revisited.- Session 3.- Language-Based Abstraction Refinement for Hybrid System Verification.- More Precise Partition Abstractions.- The Spotlight Principle.- Lattice Automata.- Invited Tutorial.- Learning Algorithms and Formal Verification (Invited Tutorial).- Session 4.- Constructing Specialized Shape Analyses for Uniform Change.- Maintaining Doubly-Linked List Invariants in Shape Analysis with Local Reasoning.- Automated Verification of Shape and Size Properties Via Separation Logic.- Invited Talk.- Towards Shape Analysis for Device Drivers.- Session 5.- An Abstract Domain Extending Difference-Bound Matrices with Disequality Constraints.- Cibai: An Abstract Interpretation-Based Static Analyzer for Modular Analysis and Verification of Java Classes.- Symmetry and Completeness in the Analysis of Parameterized Systems.- Better Under-Approximation of Programs by Hiding Variables.- Invited Tutorial.- The Constraint Database Approach to Software Verification.- Session 6.- Constraint Solving for Interpolation.- Assertion Checking Unified.- Invariant Synthesis for Combined Theories.